One Platform. Every Asset. Every Risk.

See everything you own. Secure everything you see.

A modular platform for asset visibility, vulnerability management, and IT operations, built on one inventory so security and IT finally work from the same facts.

Foundation inventory Independently licensable modules On-premises Windows deployment
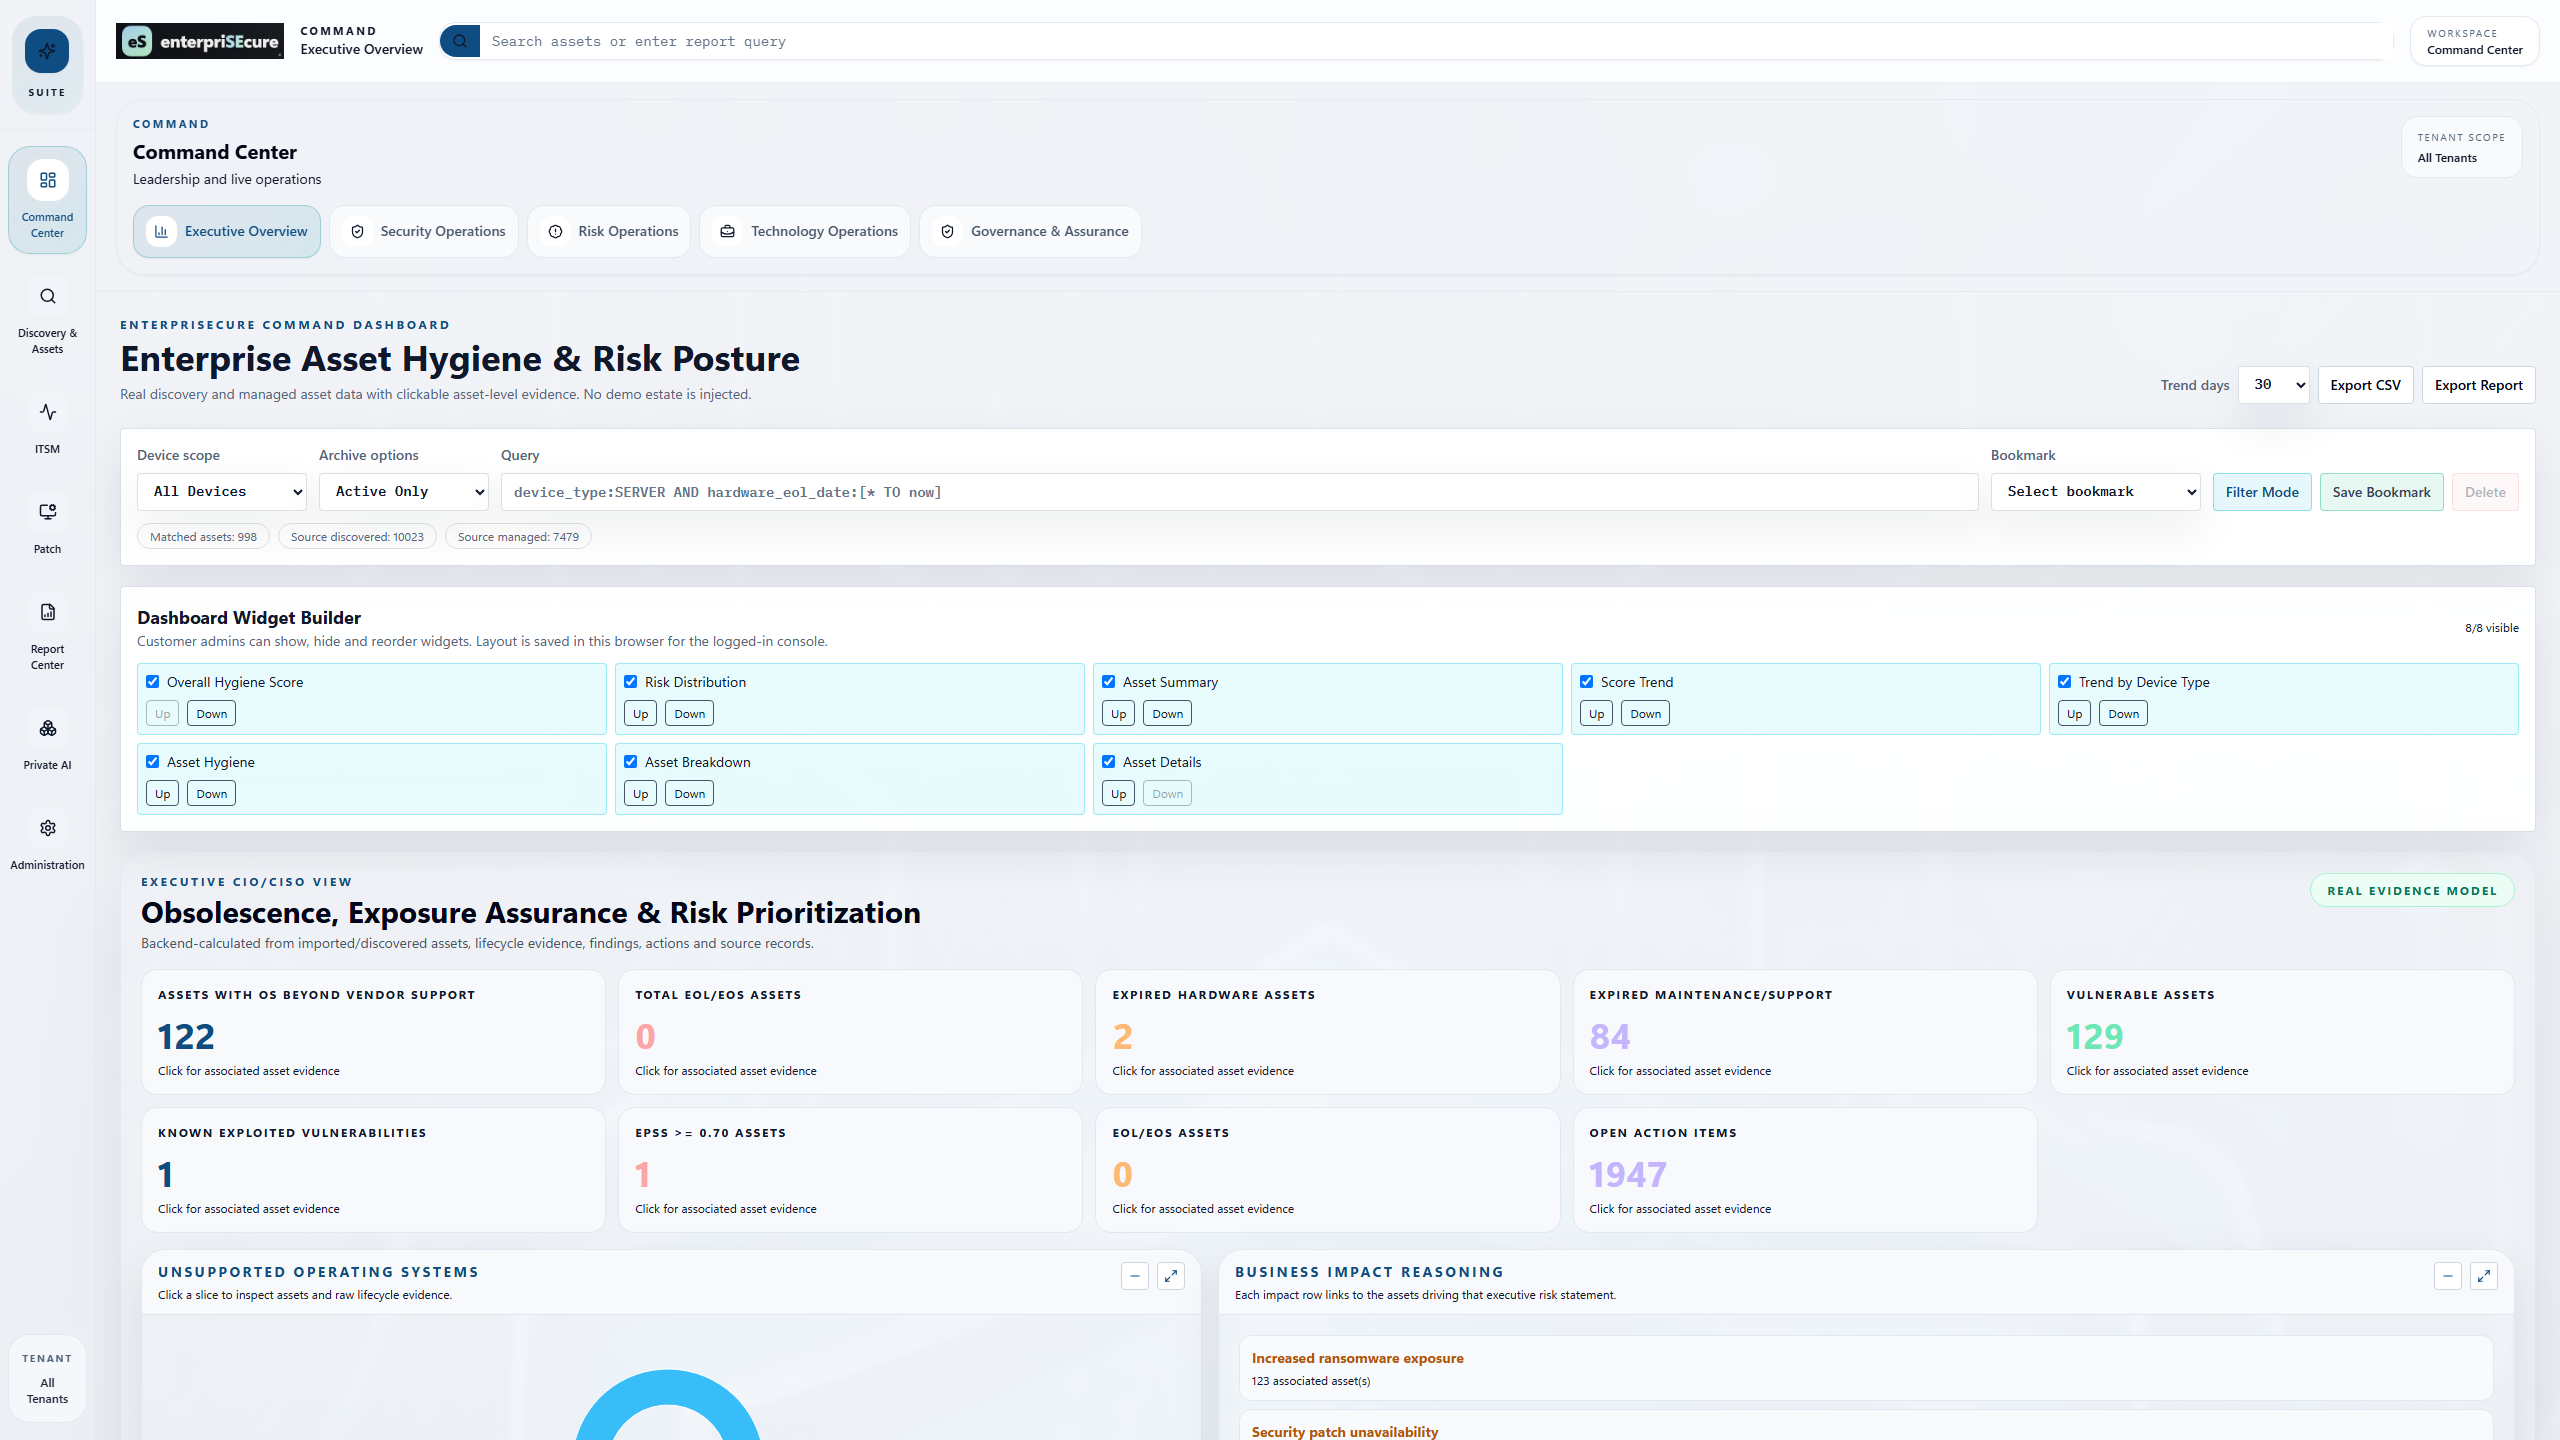
enterpriSEcure executive dashboard
Executive Asset and Risk Assurance Coverage, exposure, governance, and remediation posture in one operating view.
S

I lead Security

Reduce attack surface, detect threats faster, and prove compliance without stitching together tools that do not agree on asset truth.

See Security Solutions
I

I lead IT Operations

Know what you own, what it costs, and where the risk is before an audit, a renewal, or an outage forces the question.

See IT Operations Solutions

Platform Overview

Eighteen modules. One inventory. Your choice how many you need.

Platform Foundation is the required data layer. Every other module is optional and independently licensable, but each one reads from and writes back to the same asset, software, identity, vulnerability, and audit evidence.

Visibility and Governance Reporting and Dashboards, Admin and Security, audit evidence, RBAC, tenant controls
Asset and Software Governance HAM, SAM, ITAM, SBOM, License Management
Security Operations VMDR, Log Management, SIEM, SOAR
IT Service and Operations ITSM, Patch Management, Configuration Management, ITOM
Platform Foundation Discovery, Intelligence and Enrichment, canonical inventory, proof links, lifecycle context

How It Works

From "we think we know" to "we know."

1. See itDiscovery and Intelligence build the inventory automatically.
2. Govern itHAM, SAM, ITAM, SBOM, and licensing turn raw inventory into managed assets.
3. Find the riskVMDR, Log Management, SIEM, and SOAR prioritize exposure and response.
4. Run itITSM, Patch, Configuration, and ITOM operationalize remediation and service health.

Foundation Layer

The inventory everything else is built on.

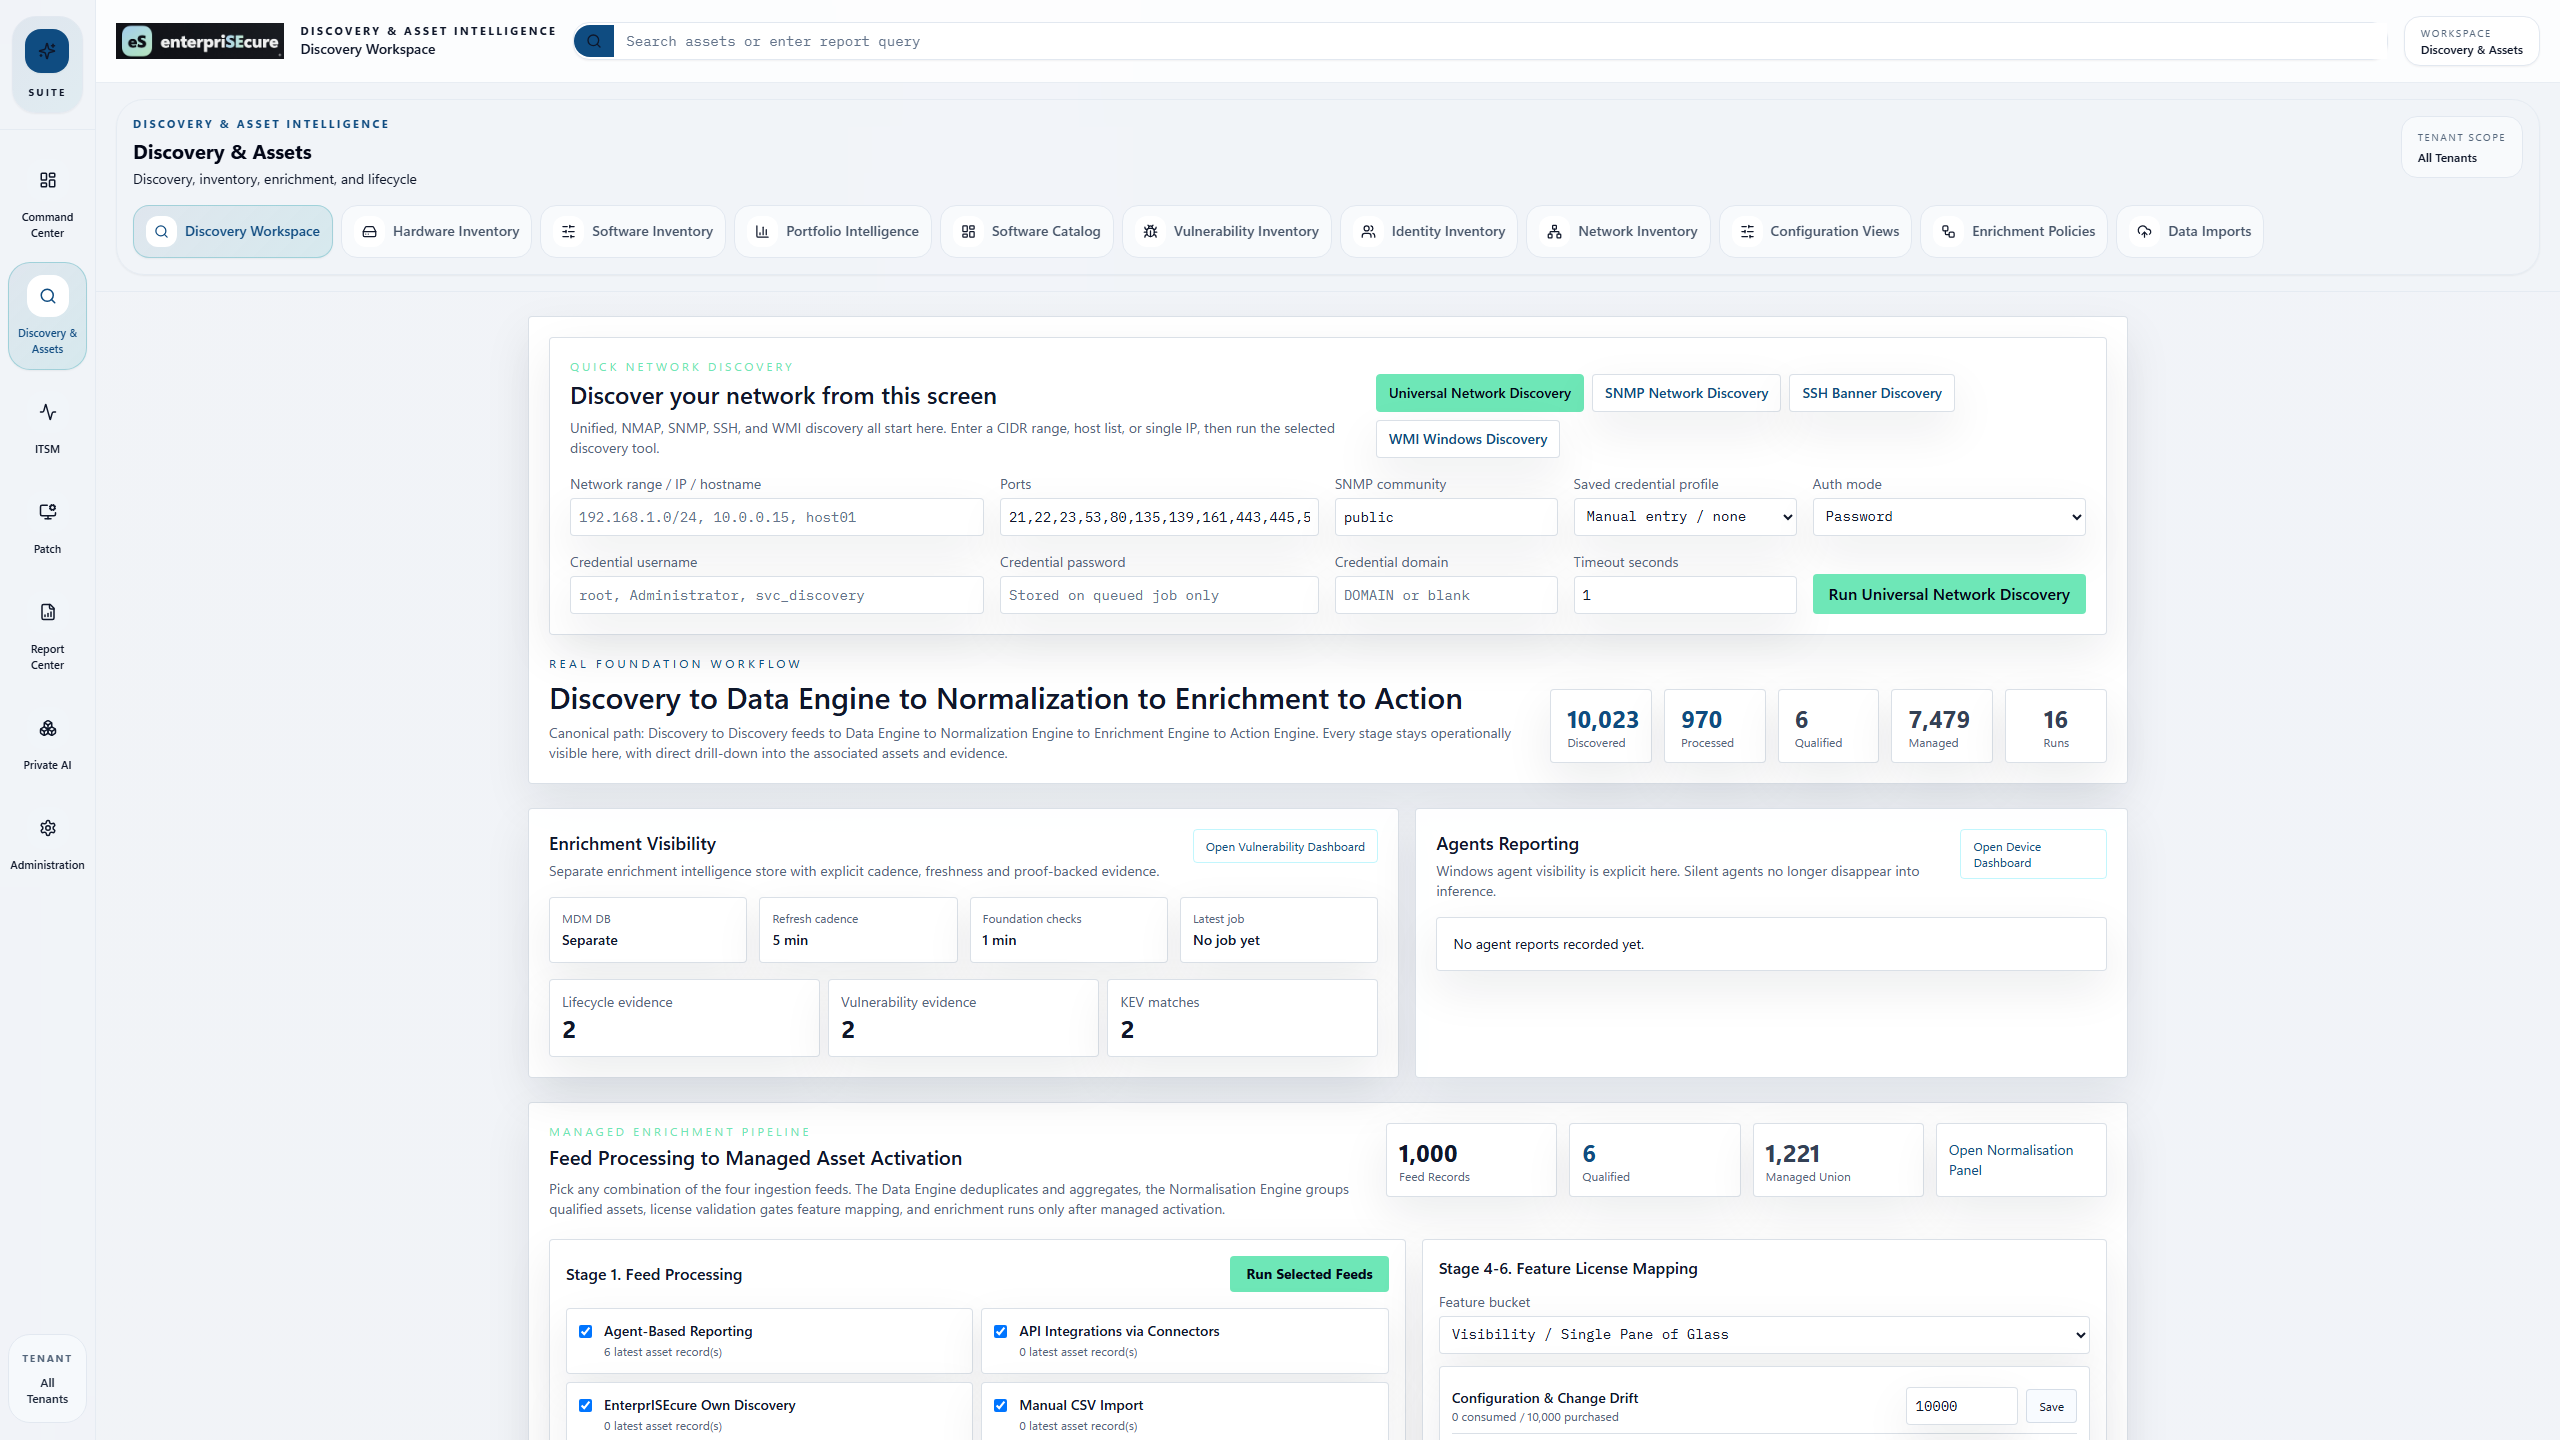
enterpriSEcure unifies endpoint agent evidence, network discovery, authenticated WMI/SSH/SNMP inspection, imports, enrichment sources, and user-entered governance data into one canonical asset record.
  • Deduplicates asset identity across agents, Nmap, SNMP, WMI, SSH, and imports.
  • Stores lifecycle proof for hardware, firmware, OS, software, vulnerabilities, and ownership.
  • Feeds ITSM tickets, patch campaigns, reports, and security analytics from the same records.
Discovery workspace

Modules

Pick the modules that solve today's problem. Add the rest when ready.

Asset and Software Governance

Control device lifecycle, software risk, entitlements, procurement, ownership, and software supply chain exposure.

Security Operations

Prioritize vulnerabilities, centralize logs, detect threats, and automate response using asset context.

IT Service and Operations

Turn findings into service workflows, change gates, patch deployments, baselines, and operational health.

Visibility and Governance

Deliver executive dashboards, scheduled reports, audit evidence, RBAC, tenant controls, and administration.
ITAMUnified hardware, software, cost, ownership, contract, and lifecycle register.
SBOMComponent inventory, dependency risk, CVE correlation, and supply chain reporting.
License ManagementEntitlements, usage, renewal timelines, true-up exposure, and customer license controls.
SOARApproval-aware security playbooks for containment, notification, ticketing, and evidence capture.
Configuration ManagementBaselines, drift detection, change traceability, and compliance posture.
ITOMOperational health, service dependencies, capacity signals, and ITSM-linked alerts.
Reporting and DashboardsExecutive, analyst, operator, compliance, scheduled, and export-ready reporting.
Admin and SecurityRBAC, audit, tenant controls, secrets, installer health checks, and platform governance.
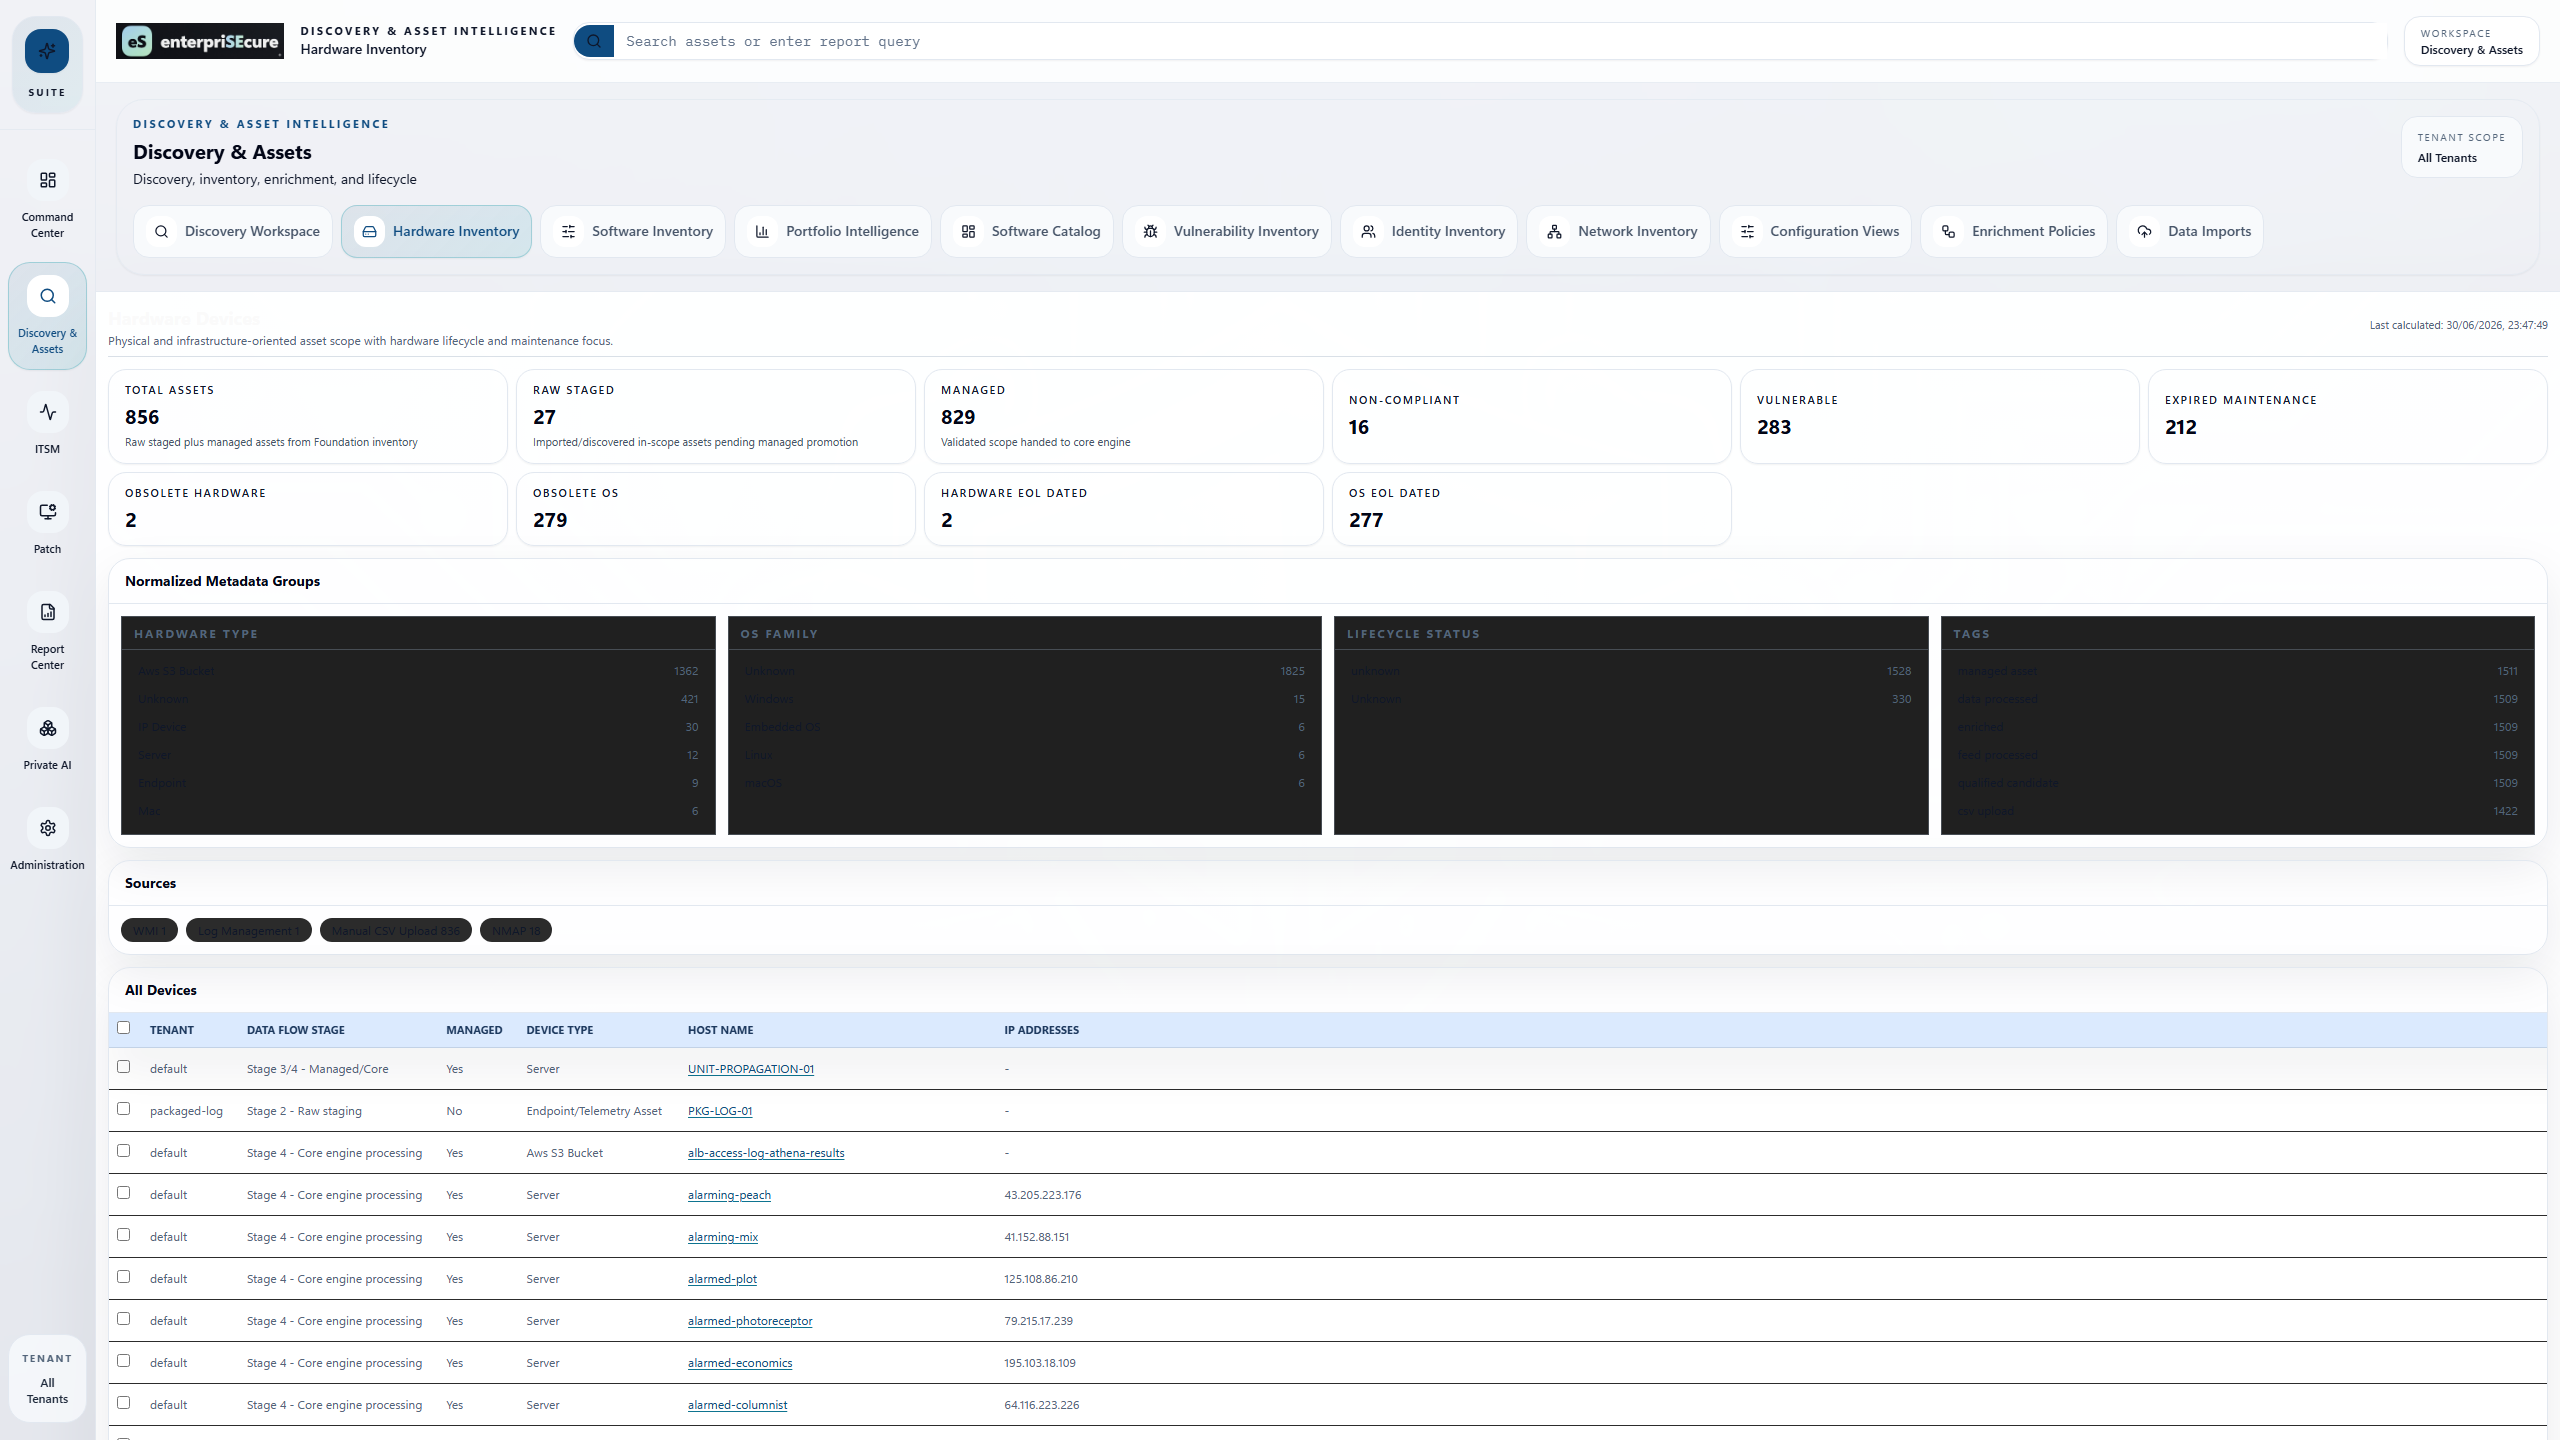
Hardware asset lifecycle dashboard

HAM

Know every device and its full lifecycle.

Track hardware from procurement to disposal with custody, spare pool, stockroom, vendor, recycler, certificate, and proof history.

SAM

Every install. Every license. Every risk, in one place.

Normalize noisy software inventory, identify unauthorized and expired software, create deletion requests, and prove audit traceability.
Software catalog dashboard

Security Leader Outcomes

Reduce attack surface and prove continuous control.

Reduce attack surfaceUnknown assets, unsupported software, exposed services, and exploitable vulnerabilities in one queue.
Accelerate detectionLogs, SIEM detections, asset criticality, and threat intelligence connected to the same inventory.
Prove complianceAudit-ready evidence for vulnerability SLAs, patch status, lifecycle risk, and governance actions.
Unify fragmented toolsFoundation data replaces tool-by-tool reconciliation and stale exports.
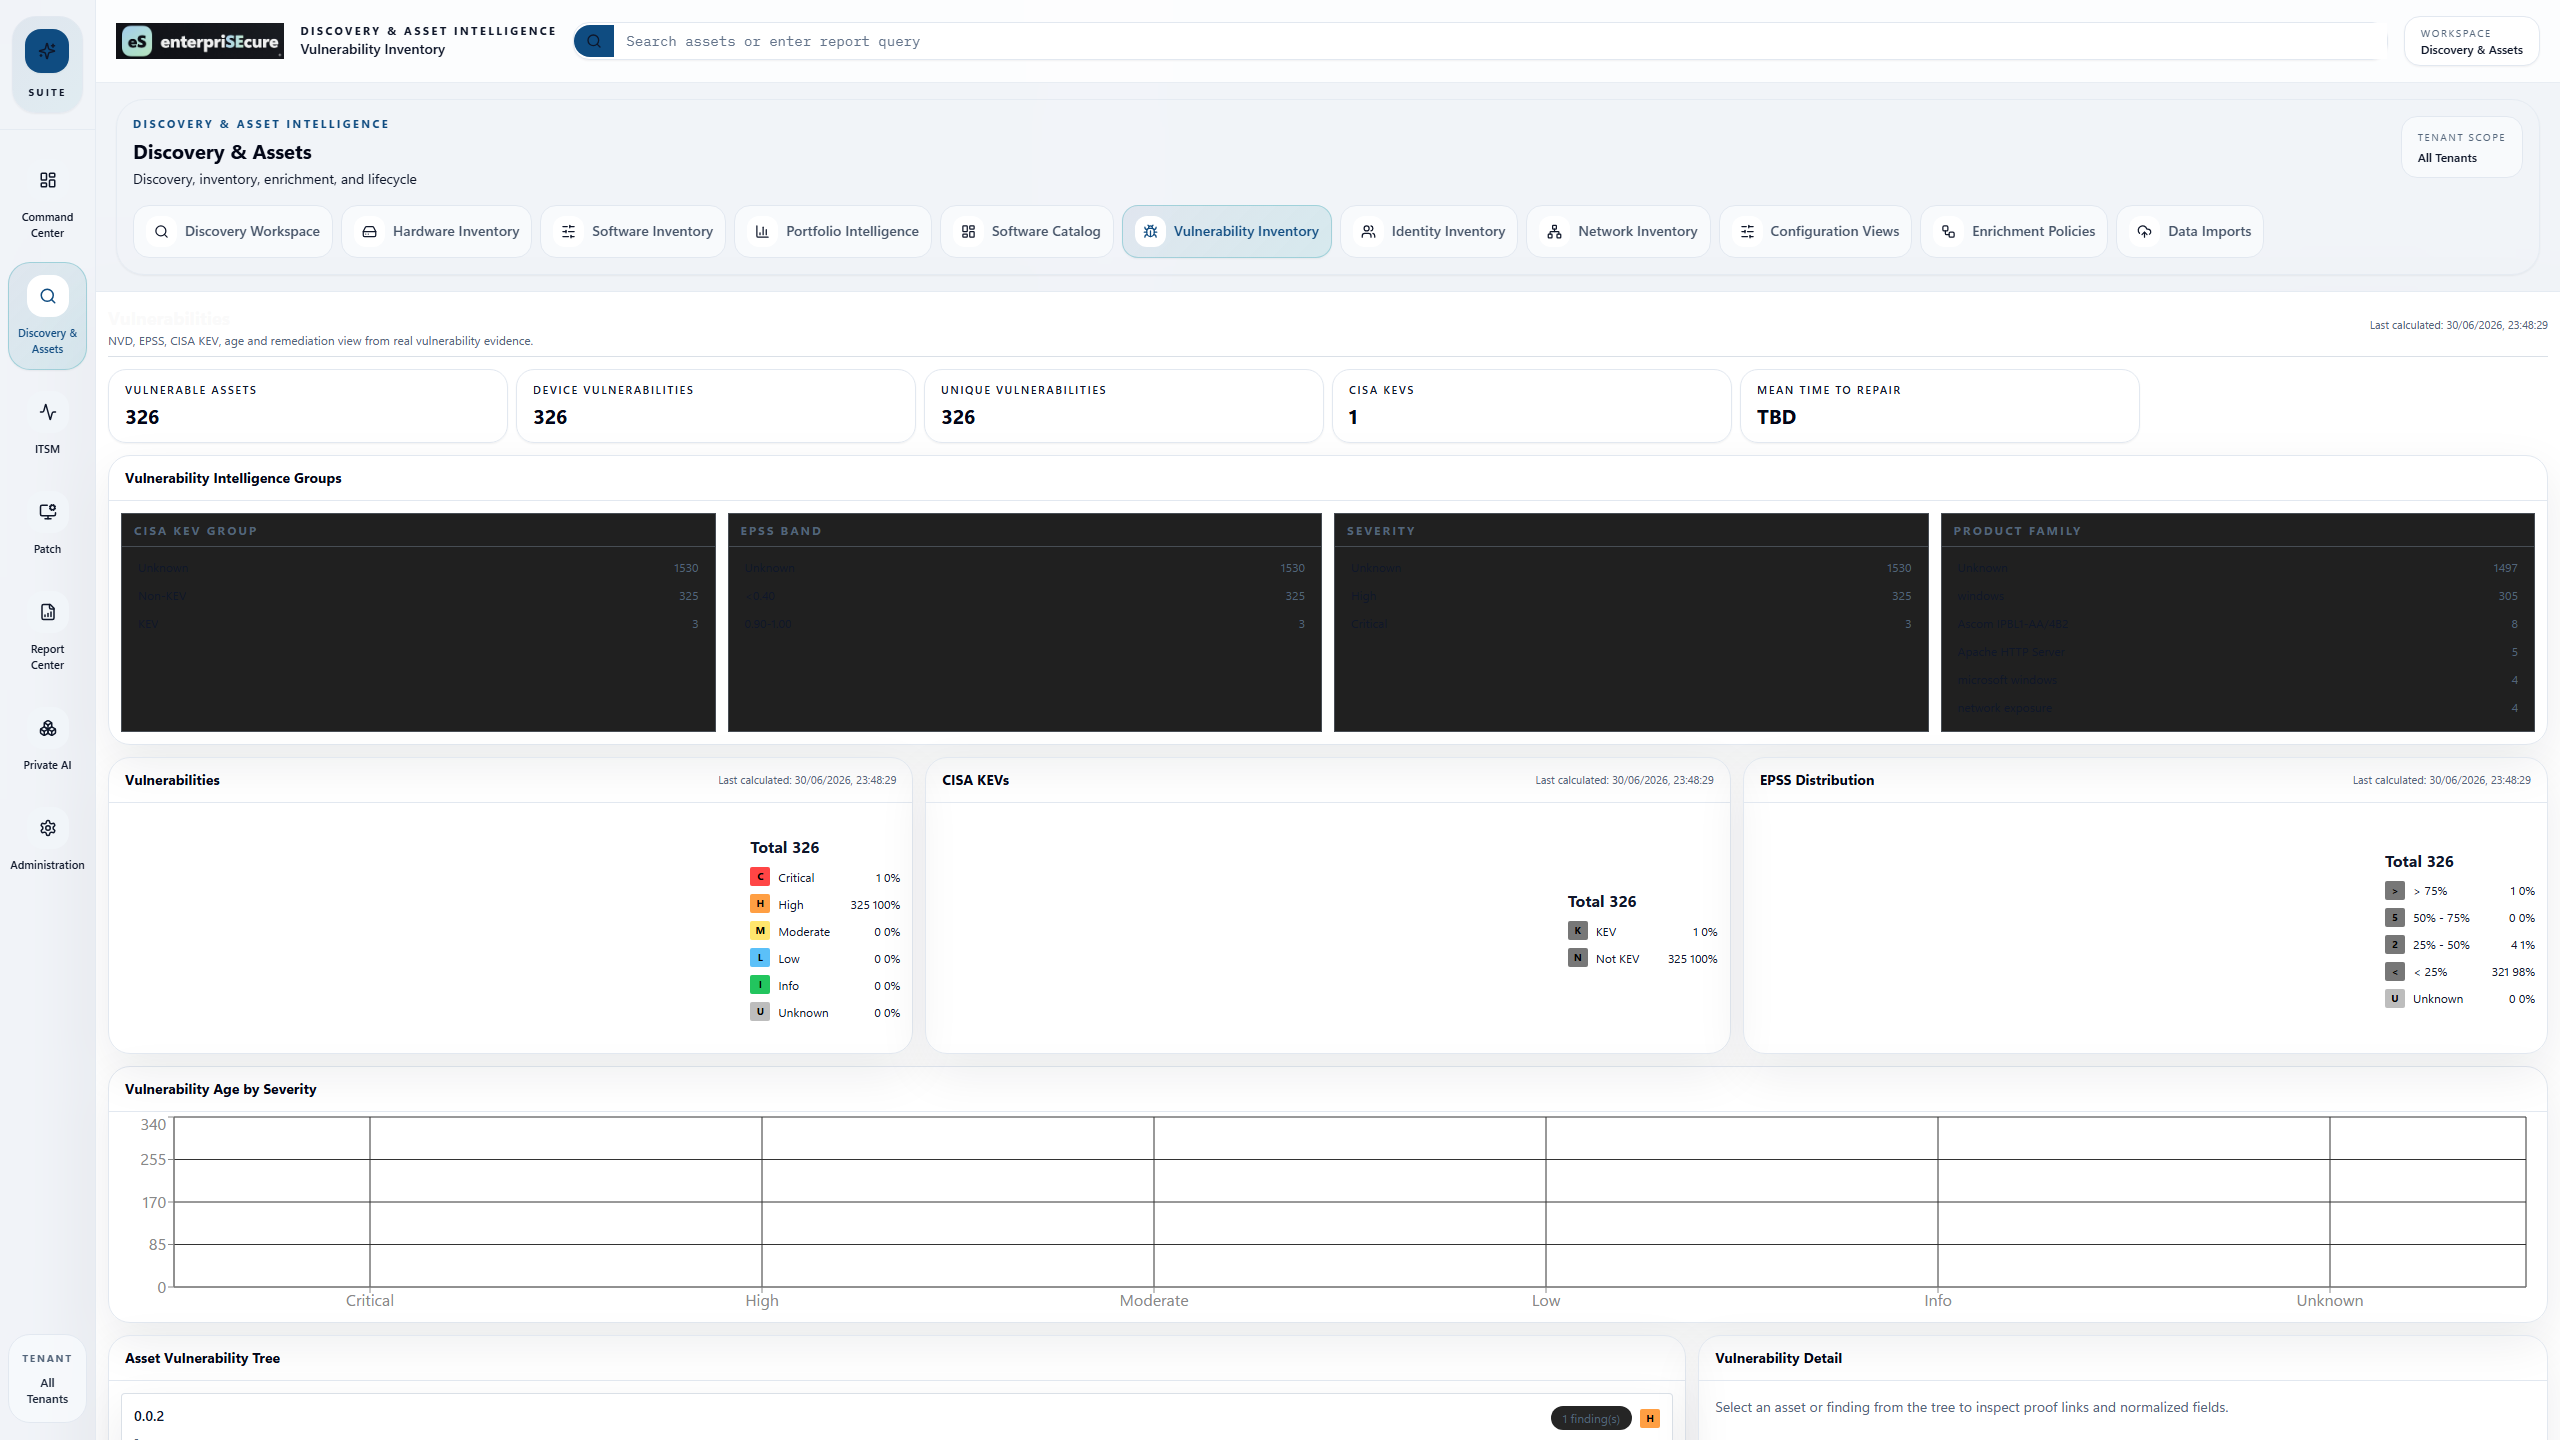
Vulnerability management dashboard

Log Management

Every log, searchable, governed, retained, and routed.

CollectWindows, Linux, authentication, access, network traffic, DNS, email, proxy, WAF, cloud, IAM, PKI, backup, patch, EDR, software install, and system logs.
NormalizeParse heterogeneous events into consistent fields for search, alerting, retention, archive, and legal hold.
InvestigateRun business-friendly searches, pivots, timelines, and export packs across hot, warm, and archived logs.
RouteCreate alerts, ITSM tickets, SOAR actions, webhook notifications, and evidence packages from log detections.

SIEM and SOAR

Correlate the signal. Automate the response.

SIEMCorrelation rules, MITRE-aligned detections, asset-context alert scoring, investigation queues, and governance reports.
SOARPlaybooks for containment, notification, ticket creation, approvals, and audit-ready response history.
Threat IntelDedicated database for CISA, NVD, VirusTotal, AbuseIPDB, URLhaus, and customer feed enrichment.
EvidenceEvery alert links back to assets, users, logs, vulnerabilities, and response actions.

IT Operations Leader Outcomes

Run service delivery and remediation from the same truth.

ITSM, Patch Management, Configuration Management, and ITOM inherit asset, owner, lifecycle, software, risk, and vulnerability context automatically.
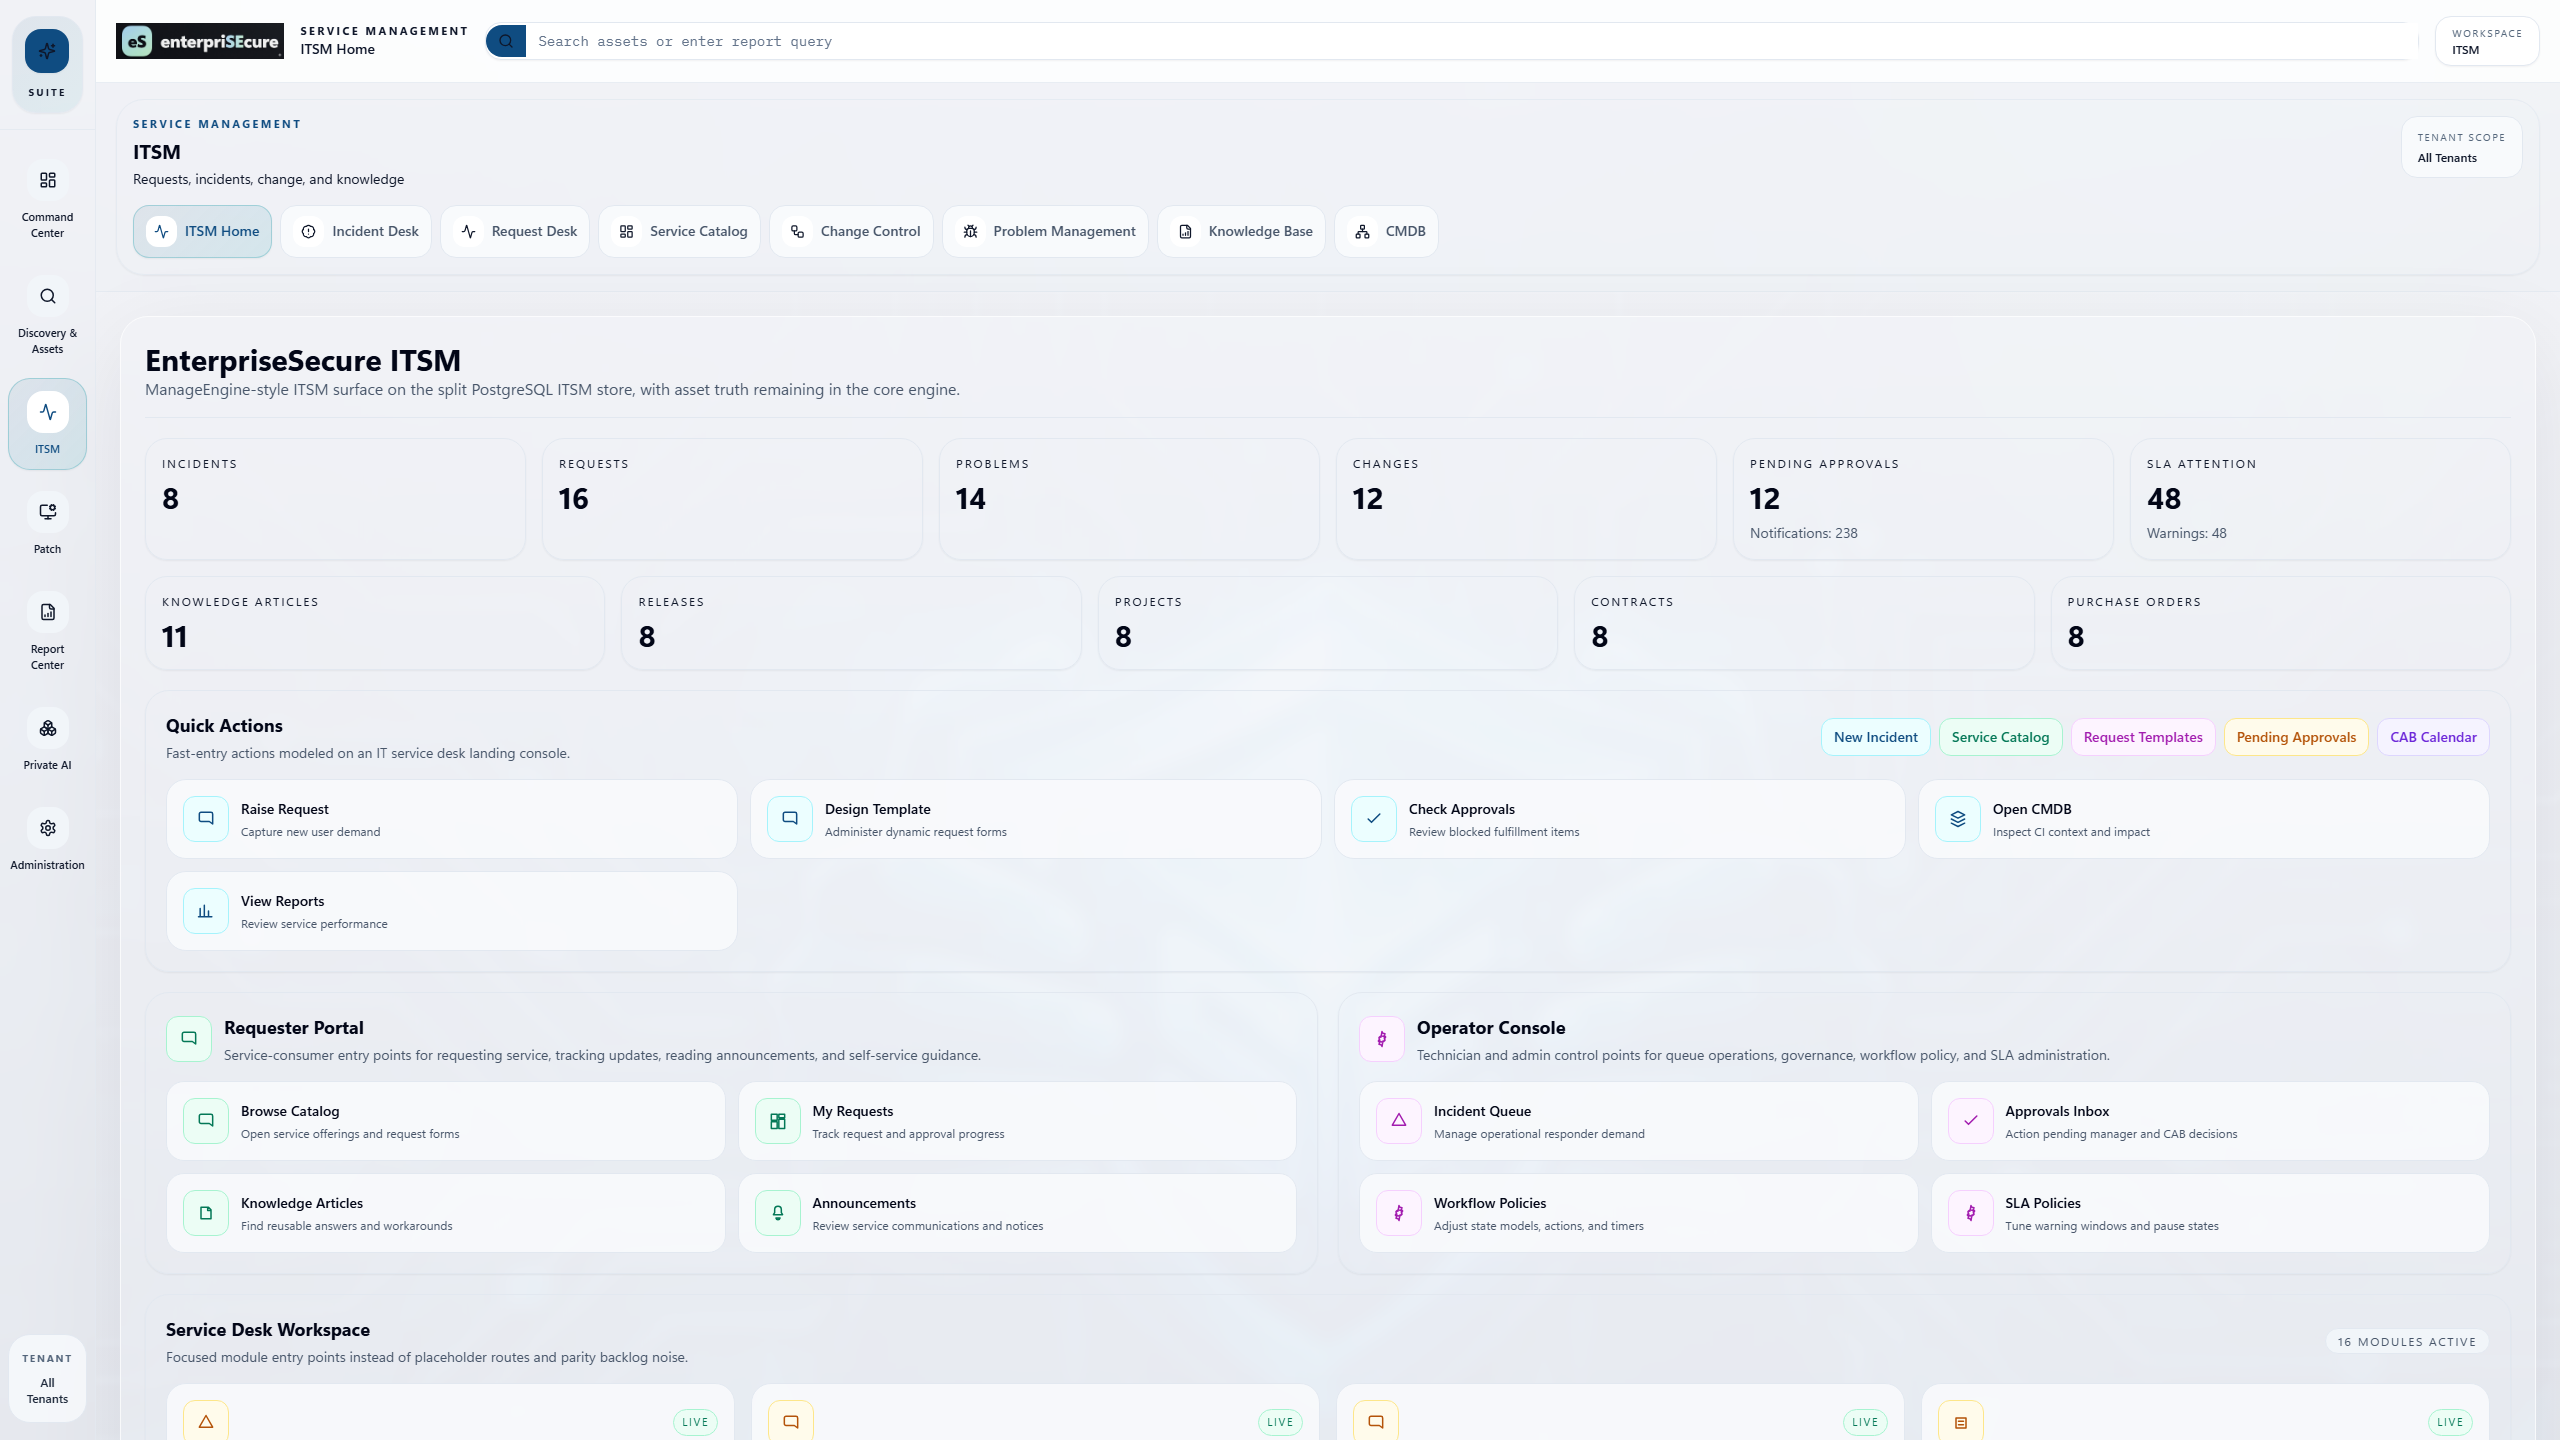
  • Auto-create incidents for EOL, EOS, critical vulnerability, and security events.
  • Auto-create service requests for unauthorized, freeware, expired, or removal-required software.
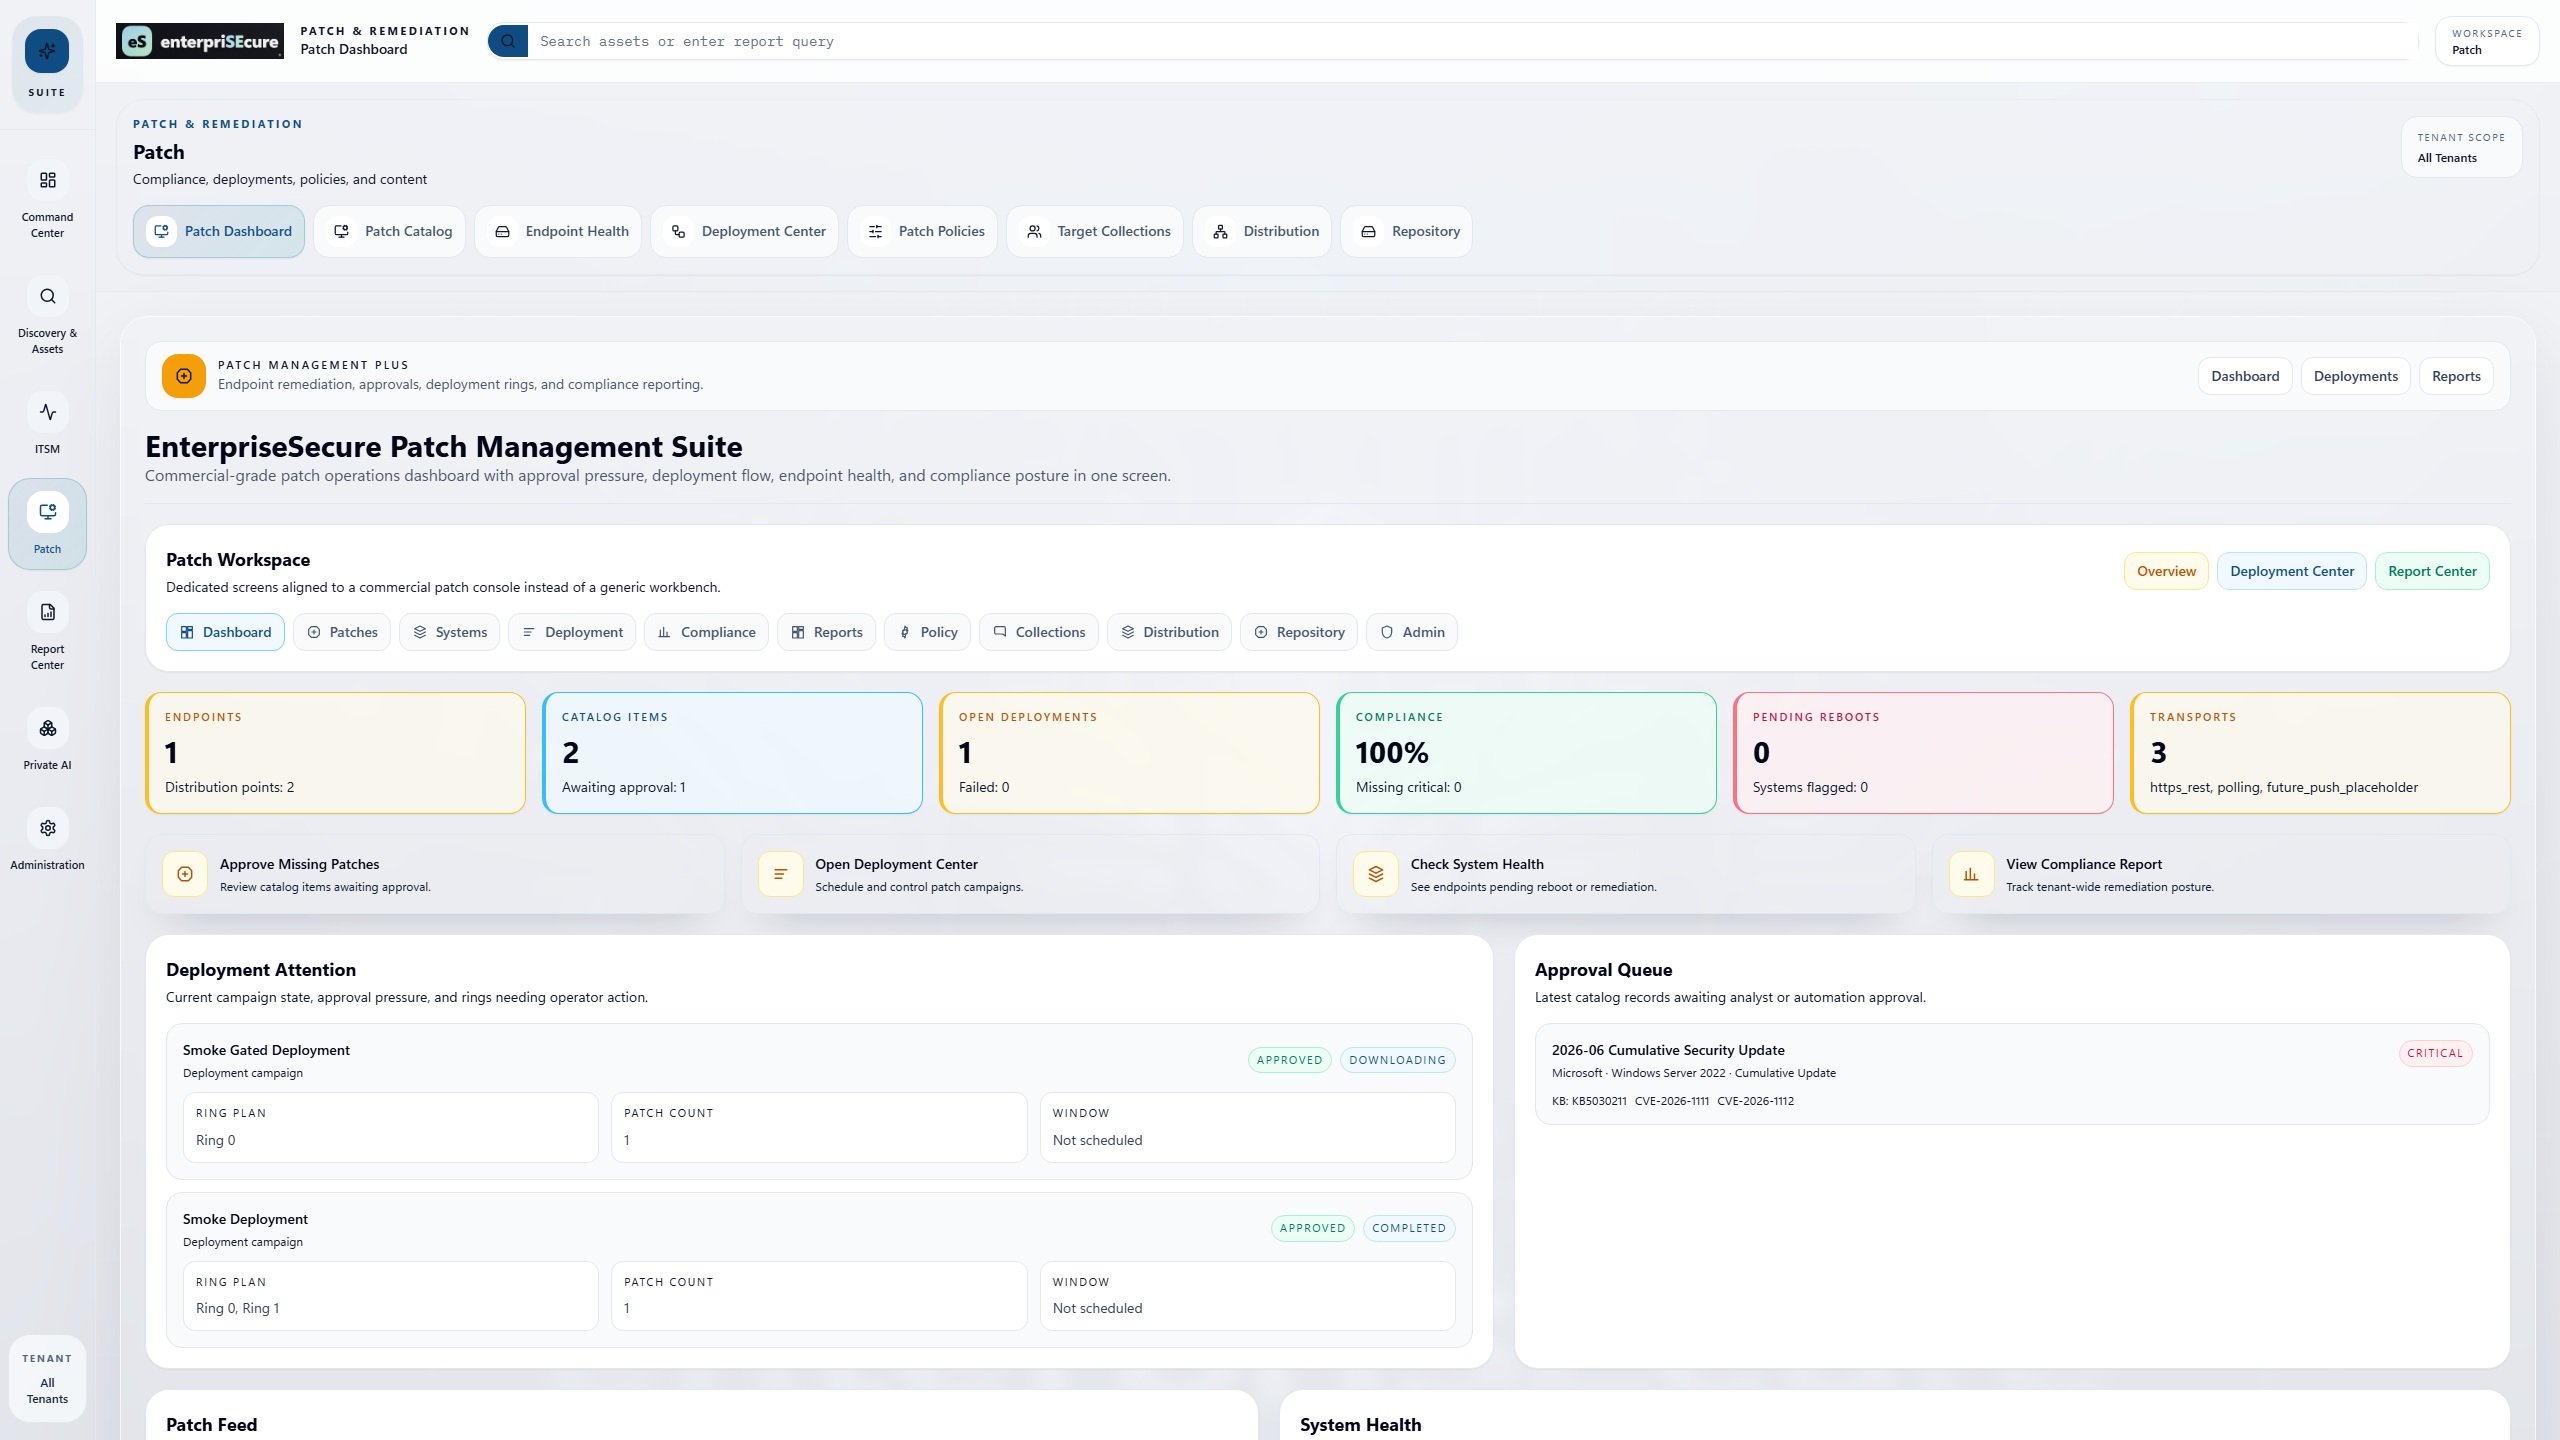
  • Gate patch campaigns through change workflows, CAB approval, maintenance windows, and deployment rings.
ITSM workspace
Patch management dashboard

Patch Management

From found to fixed, without the handoff.

Repository, checksum validation, distribution points, deployment rings, maintenance windows, ITSM change gate, compliance, and rollback-ready workflow.

Customers

Built for teams that need proof, not another disconnected console.

"We needed one place to prove which assets existed, which were unsupported, and which vulnerabilities mattered first."

CISO persona, regulated enterprise

"The value is not just discovery. It is that tickets, patches, custody, and reports use the same asset truth."

IT Operations Director persona

"Analysts stop reconciling exports and start working from linked evidence."

Security operations practitioner persona

Partners and Integrations

API-first integration model for enterprise ecosystems.

Technology partners, channel partners, MSSPs, identity providers, vulnerability feeds, SIEM sources, ITSM systems, CMDB tools, patch catalogs, and OEM lifecycle sources can be integrated through governed connectors.

MicrosoftNVDCISA KEVVirusTotalAbuseIPDBURLhausPostgreSQLClickHouseWebhookTeamsSlackREST API

Resources

Support every buyer, evaluator, operator, and administrator.

Resource CenterWhitepapers, datasheets, webinars, and solution briefs.
DocumentationDeployment guides, admin guides, module guides, API references, and support runbooks.
API and Developer HubIntegration guides, event schemas, auth patterns, and automation examples.
GlossaryHAM, SAM, ITAM, VMDR, SBOM, SIEM, SOAR, ITOM, EOL, EOS, KEV, EPSS, and more.

Pricing

Start with one module. Or start with five.

Foundation is the required base layer because every module needs the same inventory. Every other module is quoted independently so teams can adopt based on actual priority, not forced suite bundling.

Commercial model Foundation plus selected modules Server, optional node, worker, and agent deployment roles Third-party UAT package and enterprise support available Request Pricing

Trust Center

Security controls designed into the platform and the deployment.

Role-based access, tenant isolation, audit logging, encrypted secrets, HTTPS readiness, upload controls, PostgreSQL-backed persistence, installer health checks, and evidence-first reporting.

RBACAudit logsTenant controlsSecrets handlingHTTPS readyUpload controlsDatabase indexesWorker isolation

Book a Demo

Talk to us about your starting point.

Choose your first module set, validate the foundation inventory, and plan a practical enterprise rollout.